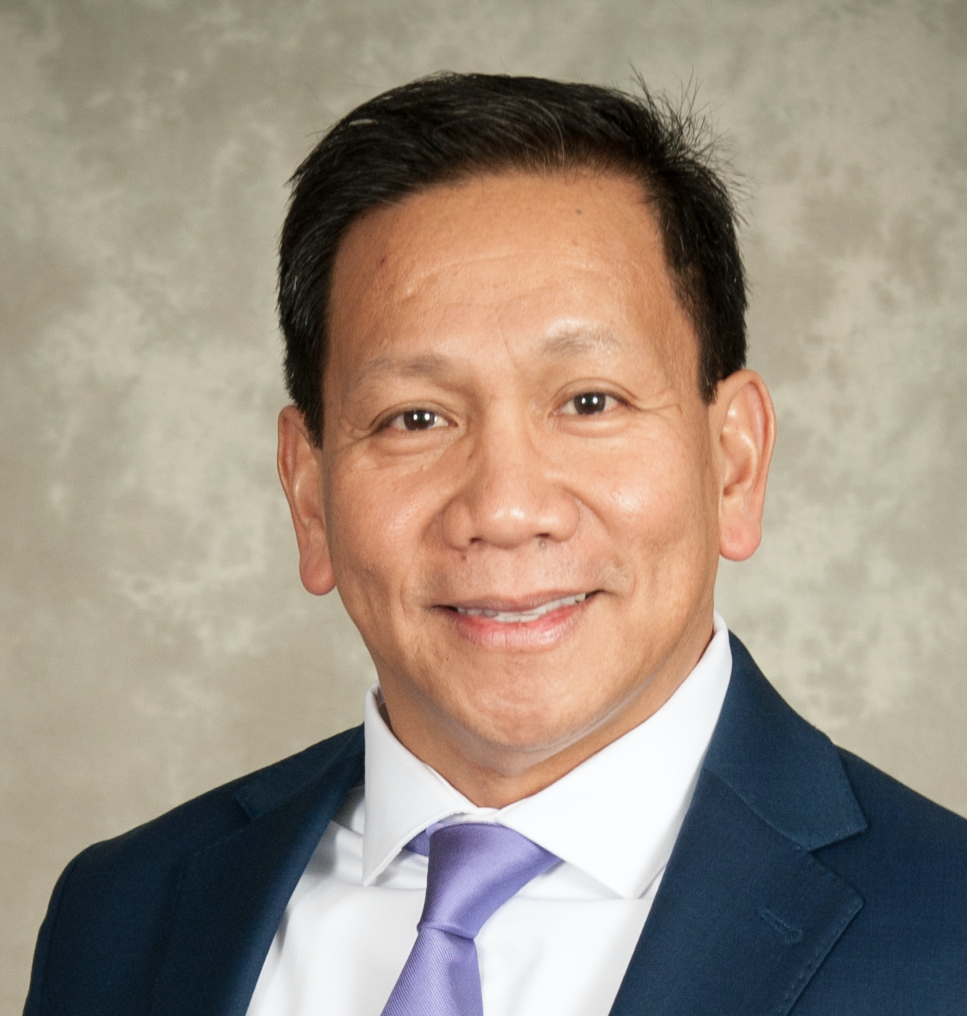
Leonard Casiple: Challenging CARVER: A Qualitative Expert Study on the Effectiveness of the CARVER Matrix in a Cyber Environment and Its Claimed Capability to Predict Adversarial Target Selection
🔗 linkedin.com/in/leonardcasiple
Research Focus: Domestic Critical Infrastructure Resilience • Cybersecurity Policy
“Challenging CARVER: A Qualitative Expert Study on the Effectiveness of the CARVER Matrix in a Cyber Environment and Its Claimed Capability to Predict Adversarial Target Selection”
What research challenge did your dissertation address?
My research set out to improve the resilience of all 16 domestic critical infrastructure sectors by examining whether a decades-old vulnerability assessment framework still holds up in a modern cyber environment, and whether it can genuinely help find and close vulnerabilities before adversaries find them.
What inspired you to pursue this research?
I learned the CARVER Matrix, short for Criticality, Accessibility, Recognizability, Vulnerability, Effect, and Recoverability, in 1997 as a student in the U.S. Army Special Forces Qualification Course. It has since become the official U.S. government-endorsed vulnerability assessment framework for critical infrastructure. While preparing a class presentation on the water sector in 2024, a question occurred to me: how accurate is CARVER’s ‘Recoverability’ assessment when data has been taken for ransom and returned? In the physical world, recoverability can be assessed accurately because rebuilding happens under observation. But recovered data may come back embedded with additional malware, making that assessment unreliable in a cyber environment. That question led me to examine whether the other CARVER dimensions, and the framework’s broader claim to predict adversarial target selection, hold up the same way.
What did your research find, and what is its impact?
The research affirmed that the CARVER Matrix remains an appropriate framework, but found that organizational and functional silos between risk managers and cybersecurity experts prevent real-time information sharing, creating information asymmetry and less effective policies. I also found that CARVER’s prediction failures mirror a broader, industry-wide shortcoming: models fail to account for cognitive biases and rarely question the results of their own scale-scoring systems. My central recommendation is that critical infrastructure should be approached holistically rather than as separate physical and cyber attributes, since what happens in one affects the other simultaneously, requiring a new ‘hybrid’ assessment and governance model.
“Critical infrastructure should be approached holistically rather than as separate physical and cyber attributes, since what happens in one affects the other simultaneously.”
Leonard Casiple